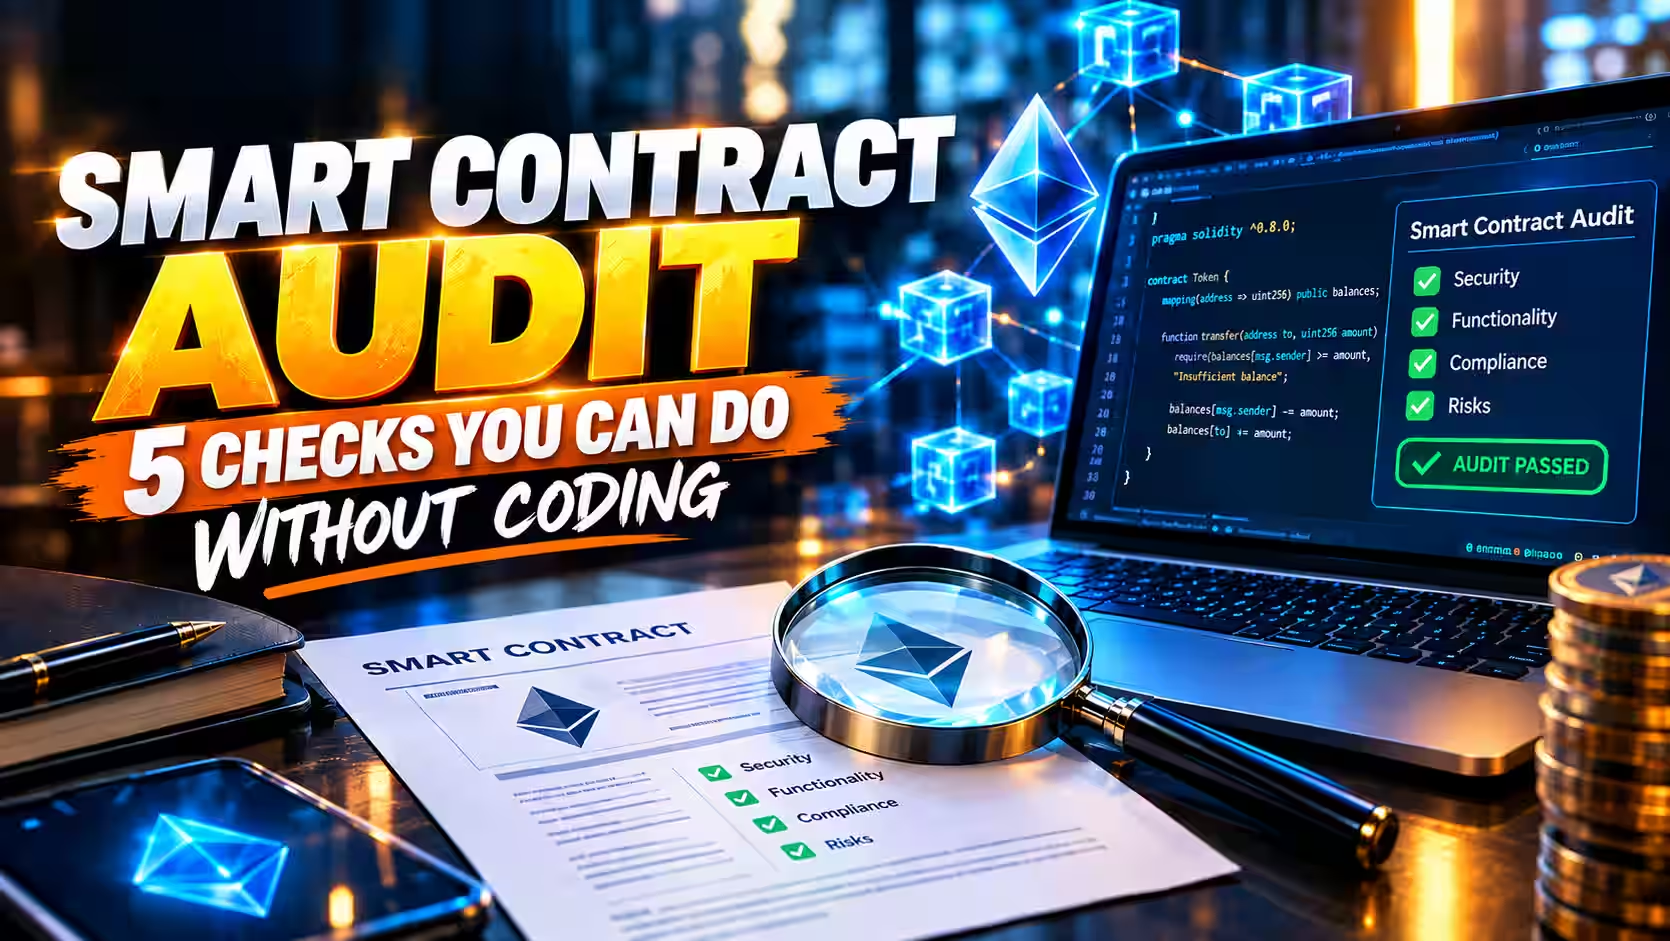
How to Audit a Smart Contract (Without Being a Developer)
Fintech Analyst · Founder of Tech Capital Hub
Marcus has spent more than a decade researching blockchain, DeFi, and financial technology. In this guide, he breaks down how to read a smart contract audit without coding knowledge, what red flags actually matter, and how investors can verify whether a DeFi protocol’s security review is credible before putting money at risk.
Let me be straight with you. The first time someone told me to “check the audit” before putting money into a DeFi project, I nodded like I understood. I didn’t. I opened the PDF, stared at a wall of Solidity code and phrases like “reentrancy vulnerability” and “integer overflow,” and closed it in under a minute.
If that sounds familiar, you’re not alone — and you don’t need to feel bad about it. Most retail investors in the US are getting into DeFi without a computer science background, and almost nothing in this space is built to help them evaluate risk clearly. That’s a problem, because unlike a brokerage account or a bank deposit, there’s no SIPC protection, no FDIC insurance, and no regulator stepping in when a protocol gets drained.
The due diligence burden falls entirely on you. And one of the most important things you can do is learn how to look at a smart contract audit — not read the code, just read the report. Here’s how to do that, from start to finish, in plain English.
Your Quick Audit Checklist
Run these five simple checks before you put a single dollar into any DeFi protocol.
-
Who did the audit?
Look for known, credible firms like Trail of Bits, OpenZeppelin, or Spearbit. A name you’ve never heard of is a reason to dig deeper.
-
When was it done?
An audit older than 12 months with major code changes since is basically worthless. Fresh matters here.
-
What did they find?
Scan for Critical and High severity findings. These are the issues that put your money directly at risk.
-
What got fixed?
Check the “Action Taken” column. Fixed is good. Acknowledged means they knew and left it — that’s a warning.
-
Does the code match?
Confirm the audited commit hash matches the contract deployed on-chain. If they don’t line up, the audit doesn’t count.
If a project can’t clearly answer all five, treat it as a red flag. Simple as that.
Quick Answer: What Is a Smart Contract Audit?
A smart contract audit is an independent security review of the code that runs a blockchain protocol. To evaluate one without coding skills, check the executive summary, the severity of findings, what the team actually fixed, who performed the audit, how recent it is, and whether the deployed code matches the reviewed version. Those five checks tell you more than any “audited” badge on a project’s homepage ever will.
What a Smart Contract Audit Actually Is?
A smart contract is code that runs automatically on a blockchain once certain conditions are met. No human approves the transaction. It controls the rules of a DeFi protocol — who can withdraw money, when, how much, and under what conditions. When you deposit funds into a lending protocol or a liquidity pool, you’re trusting that code to handle your money correctly.
A smart contract audit is when an independent security firm reviews that code before it goes live, looking for real vulnerabilities. Not typos. We’re talking logic flaws that let attackers drain the protocol, admin backdoors a developer could exploit, and edge cases that break the protocol’s economic rules.
Think of it like getting a home inspection before you buy. You’re not climbing into the crawl space yourself — but you read the inspector’s report and decide whether the findings are dealbreakers. That’s your job here. The inspector is the audit firm. The report is what you’re evaluating.
Table of Contents
Why This Actually Matters for US Investors
In 2025 alone, over $3.4 billion was lost to smart contract exploits and hacks, according to research tracked by Immunefi. For US investors, that number hits differently — because when a DeFi protocol gets drained, there’s no customer service line to call, no wire transfer reversal, and often no legal recourse at all. The money is gone.
What makes it worse: not all of these losses came from unaudited protocols. Some of the biggest hits came from projects that had been reviewed.
The $1.4 billion Bybit hack in February 2025 is the most important example to understand. The attack had nothing to do with the smart contract itself. It exploited the signing infrastructure — the off-chain tools developers used to authorize transactions. The audit covered the contract code. The rest of the system was never reviewed. That gap alone cost users more than a billion dollars.
The Cetus Protocol, which lost over $200 million, had been audited too. The problem was a math error in its concentrated-liquidity calculations — the kind that formal verification might have caught, but a standard code review missed.
The takeaway isn’t “audits are useless.” It’s that a checkbox audit and a real security review are two very different things — and most people can’t tell them apart. This guide will help you do exactly that.
What a Security Review Actually Checks
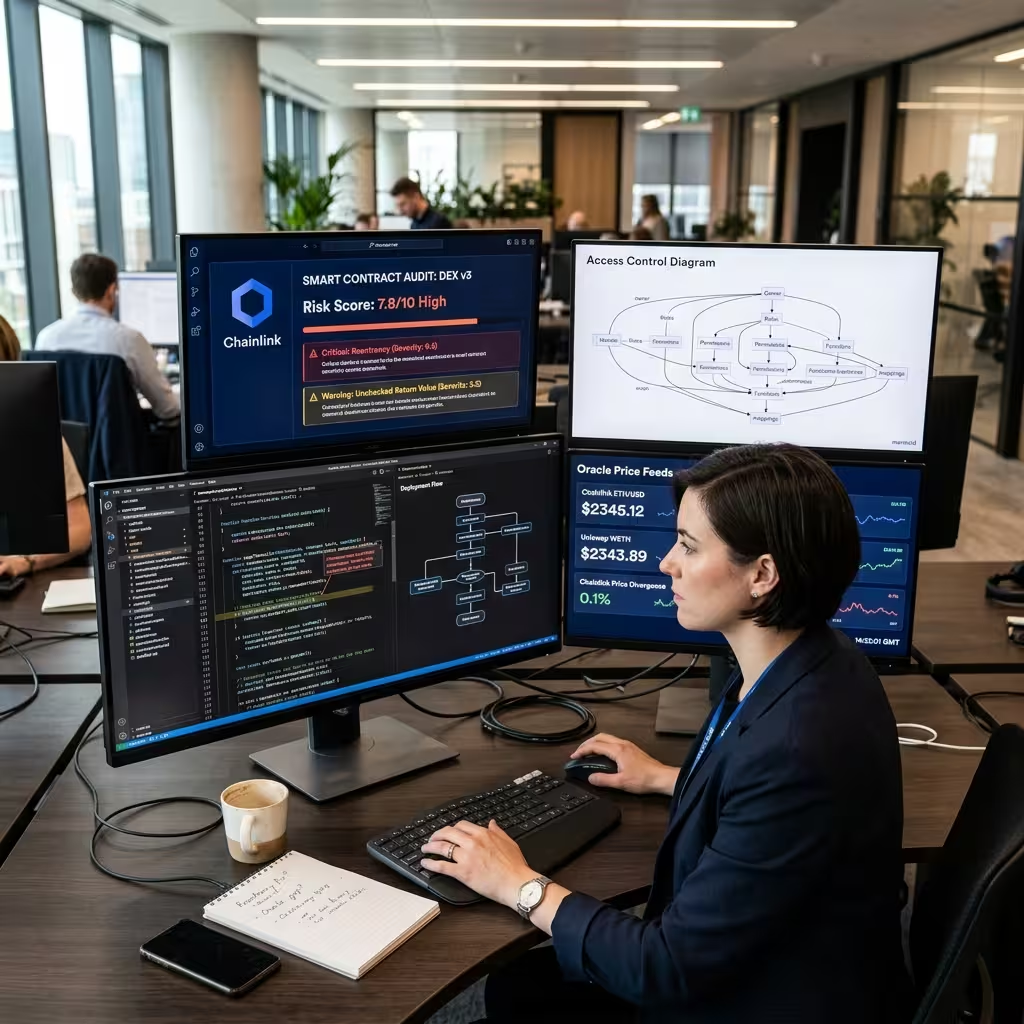
When a firm audits a smart contract, they work through several distinct vulnerability categories. You don’t need to understand the code, but you should know these categories exist — and what it means if a report flags them. Most credible auditors now map findings to the OWASP Smart Contract Top 10, the current industry-standard framework for known vulnerability classes.
Access Control
This is the leading source of losses year after year. The core question: who can call which functions? If an admin-only function doesn’t enforce the right permissions, anyone — including a malicious developer — can call it and drain the contract.
What to look for: any “Critical” or “High” finding that mentions “unauthorized access,” “missing modifier,” or “privileged role.” These are not minor issues.
Business Logic Flaws
This one is subtle. The code runs exactly as written — but the logic itself is broken. Maybe you can borrow more than your collateral should allow. Maybe a rounding error lets attackers extract tiny amounts repeatedly until the pool is empty. Catching these requires auditors to review the code against the protocol’s own documentation, not just scan for common bug patterns.
Price Oracle Manipulation
Most DeFi protocols need live price data to function. They pull it from external sources called oracles. If a protocol relies on a single price feed, an attacker can temporarily manipulate it — usually through a flash loan — and exploit the distorted reading to drain funds. Stronger protocols use decentralized feeds like Chainlink and include circuit breakers that pause activity if prices move abnormally fast.
Flash Loan Attacks
A flash loan is capital borrowed and fully repaid within a single transaction — no collateral required. An attacker can borrow tens of millions of dollars, use it to manipulate a protocol’s internal logic, then repay it — all within one block. These attacks aren’t always visible in the code itself. They require economic stress-testing, not just a line-by-line review. If an audit report never mentions flash loan scenarios, that’s a gap worth noting.
Reentrancy
This is the oldest and most well-documented DeFi vulnerability — and it’s still showing up in reports. It’s how the 2016 DAO hack worked: an attacker calls a withdrawal function, and before the contract updates the balance, they call it again. And again. Looping until the funds are gone. Every credible audit checks for this specifically. If a report flags reentrancy and marks it “Acknowledged” without a fix, that’s a hard stop.
How to Read an Audit Report Without Writing a Line of Code
Here’s the part most guides skip over. Let’s go step by step.
Step 1: Find the Executive Summary
Every legitimate audit report starts with one. It tells you the scope of what was reviewed, the review dates, and the commit hash — the exact version of the code that was audited. That commit hash matters more than most people realize. It should match the contract that’s actually deployed on-chain. If a project changed the code after the audit and before launch, the report is measuring something that no longer exists.
Step 2: Look at the Severity Breakdown
Audit findings are classified into tiers:
- Critical — Assets are at immediate risk. Must be fixed before launch.
- High — Exploitable under specific conditions. Fix required before mainnet.
- Medium — Could cause logic failure. Should be addressed.
- Low — Minor inefficiencies, not urgent.
- Informational — Style or documentation notes only.
Your focus: did the audit find any Critical or High issues? If yes, what happened to them?
Step 3: Check the “Action Taken” Column
This is the most important column in the whole report, and it’s the one most investors skip. Every finding should list what the development team did in response. Options typically include “Fixed,” “Acknowledged,” or “Disputed.”
“Fixed” means the team resolved it before deployment. “Acknowledged” means they know about it and chose to ship anyway. “Disputed” means they disagree it’s a problem. Both of those warrant serious scrutiny. A protocol with two Acknowledged High-severity findings is a fundamentally different risk than one where every issue was resolved and verified.
Step 4: Check Who Did the Audit
Not all auditing firms deliver the same quality of work. The established, widely-respected names include Trail of Bits, OpenZeppelin, Spearbit, and Sherlock. Code4rena runs competitive audit contests that can surface issues a single-firm review might miss.
Be skeptical of audits from firms you can’t verify. Some projects pay for reports from low-cost shops that produce official-looking PDFs without doing real work. For context: a legitimate audit of a standard DeFi protocol — a lending market, a DEX, a staking contract — typically costs $50,000 to $100,000 and takes three to six weeks. If a project claims a thorough audit was completed in two days for a few hundred dollars, something is off.
Step 5: Check the Date
A 2021 audit has no bearing on a protocol running in 2026. The codebase may have changed a dozen times, and entirely new attack patterns have emerged since then. If the most recent audit is more than 12 months old and the protocol has shipped significant updates since, treat it as functionally unaudited and do your evaluation accordingly.
How to Verify an Audit Is Real
The project says they’ve been audited. Here’s how to confirm it yourself — without trusting their marketing page.
- Find the public report. Real audits are published. If the team claims an audit exists but won’t share it, or makes it hard to locate, that tells you everything you need to know.
- Cross-reference on a block explorer. Look up the contract address on Etherscan and open the “Contract” tab. If the source code is verified, it’s public and matches what’s deployed. If it’s unverified, you literally cannot compare the live contract to the audit report.
- Check the audit firm’s own site. Firms like Trail of Bits, OpenZeppelin, and Spearbit publish their completed work directly. If a project claims a specific firm audited them, verify it through that firm’s own records — not the project’s website.
- Match the commit hash. Compare the hash listed in the report to what’s on the block explorer. A mismatch means the audit covered code that isn’t running.
- Look for an active bug bounty. Platforms like Immunefi host bounty programs where researchers are paid to find active vulnerabilities. A project running a real bounty has ongoing financial incentive to maintain security — not just a PDF from two years ago.
Each of these checks takes under five minutes. Combined, they give you a much sharper picture of actual security posture than any badge on a homepage.
What a Smart Contract Security Review Actually Checks
When a firm does a smart contract security review, they’re looking at several layers. You don’t need to understand the code. But you should know these categories exist and what they mean when flagged.
Access Control (SC01)
This is the #1 source of losses in 2025 — $953.2 million drained from access control failures alone. It means: who can call which functions? If an admin function doesn’t require the right permissions, an attacker (or a malicious developer) can call it and drain funds.
What to look for in a report: any “Critical” or “High” finding mentioning “unauthorized access,” “missing modifier,” or “privileged role.” These are not minor issues.
Business Logic Flaws (SC02)
This one is sneaky. The code runs exactly as written — but the way it’s written breaks the economic rules of the protocol. Maybe there’s a way to borrow more than your collateral should allow. Maybe a rounding error means attackers can extract tiny amounts repeatedly until the pool is empty.
Business logic flaws require a manual review against the project’s whitepaper. Auditors call this a “Specification Review” — they check if the code actually does what the documentation says it does.
Price Oracle Manipulation (SC03)
Most DeFi protocols need real-time price data. They get it from external services called oracles. If a protocol relies on a single price source, an attacker can temporarily manipulate that price — usually through a flash loan — and exploit the distorted reading to drain funds.
Good audit reports flag single-oracle dependence. Good protocols use decentralized feeds like Chainlink with circuit breakers that pause the system if prices move too fast.
Flash Loan Attacks (SC04)
A flash loan is a loan borrowed and repaid within a single transaction. No collateral needed. An attacker can borrow tens of millions of dollars, use that money to manipulate a protocol’s logic, and repay it — all in one block.
Flash loan vulnerabilities aren’t always obvious in the code. They require economic stress-testing, not just code review. If an audit report doesn’t mention flash loan scenarios, that’s worth noting.
Reentrancy
This is the granddaddy of DeFi vulnerabilities. It’s how the DAO hack happened in 2016. Basically, an attacker calls a withdrawal function, and before the contract updates the balance, the attacker calls it again — and again — draining funds in a loop.
A good audit checks for this specifically. If a report mentions reentrancy and marks it “Acknowledged” without a fix, that’s a problem.
The Part Most People Get Wrong: Audits Don’t Guarantee Safety
Here’s the uncomfortable truth that the DeFi space doesn’t advertise loudly enough: a clean audit report does not mean a protocol is safe.
Cetus Protocol had an audit. Balancer had multiple audits. Both lost enormous amounts of user funds to vulnerabilities that either weren’t detected or weren’t fixed. For US investors accustomed to some level of institutional accountability — FINRA oversight, exchange regulations, consumer protection laws — this is a genuinely important mindset shift. In DeFi, the audit report is the closest thing to a safety signal you’ll get, and it’s an imperfect one.
The most important distinction: a smart contract audit typically covers the contract code, not the entire system surrounding it. The Bybit hack made this painfully clear. The contract itself was fine. The off-chain signing infrastructure was compromised. A contract audit says nothing about front-end security, multisig key management, deployment pipelines, or third-party dependencies. Each of those represents a real attack surface that may never have been reviewed.
An audit shrinks your risk. It doesn’t eliminate it. The right question was never “was this audited?” It’s “what did the audit find, how old is it, who did it, and what happened to everything they flagged?”
Common Red Flags Before You Commit Capital
Run through this list for every protocol you’re considering:
- The audit report isn’t public, or the team is evasive about sharing it.
- The auditing firm has no verifiable track record or published work.
- The deployed contract is unverified on Etherscan or any block explorer.
- The commit hash in the report doesn’t match the deployed version.
- Critical or High severity findings are marked “Acknowledged” or “Disputed” with no fix.
- The audit is more than a year old and the code has changed since.
- The project claims a “full audit” that was done in days for a suspiciously low price.
- There’s no active bug bounty and no other sign of ongoing security commitment.
- The report makes no mention of flash loan or oracle risk scenarios at all.
Any single item on this list is worth pausing over. Multiple items together? That’s a clear signal to walk away.
How Much Does a Smart Contract Audit Cost?
This comes up constantly, so here are the real 2026 numbers.
Audit pricing has moved away from per-line-of-code pricing to what’s called Logic Density Valuation — pricing based on the complexity of what the code does, not how many lines it takes to do it.
A 500-line zero-knowledge verifier is exponentially more complex to audit than 5,000 lines of standard token code. The auditor has to understand every possible state the code can reach, every interaction with other contracts, every edge case.
Here’s a rough breakdown:
| Protocol Type | Typical Cost | Typical Duration |
| Basic ERC-20 token or NFT | $15,000 – $25,000 | 2–5 days |
| DEX, lending, staking protocol | $50,000 – $100,000 | 3–6 weeks |
| Cross-chain bridge or ZK rollup | $150,000 – $500,000+ | 2–6 months |
If you see a new DeFi project claiming a full audit of their lending protocol for under $10,000, something is off. Either the audit wasn’t thorough, the firm isn’t credible, or the scope was limited to a small part of the codebase.
The Best Smart Contract Auditing Tools Exist — But They’re Not for You
You’ll read about tools like Slither, Echidna, Mythril, and the Certora Prover. These are real, they’re used by real auditors, and they’re genuinely powerful.
Here’s what each one does:
- Slither does static analysis — fast detection of common vulnerability patterns.
- Echidna does fuzzing — throwing thousands of random inputs at a contract to see what breaks.
- The Certora Prover does formal verification — using mathematical proofs to confirm the code can never violate its core rules.
You don’t need to run these yourself. But knowing they exist helps you ask better questions:
- Did the audit use only static analysis tools?
- Did it include fuzzing?
- Was formal verification done?
Higher-assurance audits layer multiple methodologies. Basic ones run one tool and call it done.
Frequently Asked Questions
How to read a smart contract audit report without coding knowledge? Focus on the executive summary, severity breakdown, and the “Action Taken” column for every finding. Critical and High findings that were “Acknowledged” instead of fixed are warning signs that don’t require code knowledge to recognize.
What does a smart contract audit check for? Audits check for access control failures, business logic flaws, price oracle manipulation, flash loan vulnerabilities, reentrancy attacks, and integer overflow errors. The 2026 OWASP Smart Contract Top 10 is the current industry standard for what comprehensive audits cover.
How much does a smart contract audit cost in 2026? Standard DeFi protocols (DEXes, lending, staking) cost between $50,000 and $100,000 and take three to six weeks. Basic token contracts run $15,000 to $25,000. High-complexity infrastructure like cross-chain bridges can exceed $500,000.
What are the best smart contract auditing firms in 2026? Trail of Bits, OpenZeppelin, Spearbit, and Sherlock are among the most respected. Immunefi runs the largest bug bounty platform. Code4rena and Sherlock run competitive audit contests for large codebases.
How to verify if a DeFi contract is audited? Check for a publicly available audit report, verify the contract source code on Etherscan, confirm the commit hash in the report matches the deployed code, look up the audit on the firm’s own website, and check when the audit was completed relative to any major code updates.
What is a reentrancy attack in simple terms? It’s when an attacker exploits a withdrawal function by calling it repeatedly before the contract updates the balance — essentially looping a withdrawal to drain funds. The 2016 DAO hack used this method and it remains on the 2026 OWASP Top 10 today.
The Bottom Line
You don’t need to read Solidity. You don’t need to understand the EVM. You don’t need to run fuzzing tools on your own machine.
What you need is to know what questions to ask and what the answers should look like. Who audited it. When. What they found. What got fixed. Whether the code that’s actually running matches what was reviewed.
That’s it. That’s the whole job for a non-developer doing smart contract due diligence.
The $3.4 billion lost in 2025 didn’t disappear because people couldn’t read code. A lot of it disappeared because people didn’t check — or they checked the wrong things, or they trusted a badge on a homepage without clicking through to the actual report.
Do the five checks above before you put money into anything. Every time.
Disclaimer: This article is for informational purposes only and does not constitute financial or legal advice. Smart contract investments carry significant risk including total loss of funds. Always conduct your own research before investing.
Blockchain · Editorial Integrity
Sources & Citations
Public data, audit standards, and current industry reporting behind this guide to reading a smart contract audit, evaluating DeFi security risk, and verifying whether a protocol’s review is credible.
Every key claim in this guide is grounded in public documentation, named security standards, incident reporting, and reputable industry sources. We prioritize primary technical guidance, official project documentation, security frameworks, and current reporting on DeFi exploits, verification practices, and audit methodology. Because threat patterns and protocol code change fast, always verify the latest audit status and contract version before relying on any project.
View full sources, methodology, and editorial notes
This guide was written using official blockchain documentation, recognized smart contract security frameworks, public exploit reporting, audit-industry references, and live verification tools used to inspect deployed contracts. We give preference to primary documentation, named security providers, and public technical references that directly support explanations around audit scope, severity levels, code verification, and exploit categories. Some figures and examples may change as the industry evolves. This article is educational information, not financial, investment, or legal advice.
- Smart contract risk and vulnerability categories: OWASP Smart Contract Security Project — cited as a foundational industry framework for common smart contract security risks and review categories.
- Official contract verification and on-chain review: Etherscan — cited as the primary public reference for checking verified contract code, deployed addresses, and matching reviewed code to live implementations.
- Smart contract auditing and security practices: OpenZeppelin Security Audits — cited as a recognized audit provider reference for how professional smart contract reviews are conducted.
- Independent security research and audit standards: Trail of Bits — Security Reviews — cited to support the discussion of credible audit firms, review scope, and security assessment depth.
- Competitive audits and vulnerability disclosure: Code4rena — cited as a reference for contest-based audit reviews and broader vulnerability discovery models.
- Bug bounty programs and ongoing security coverage: Immunefi — cited to support the section on bug bounties as a sign of continued security commitment beyond a one-time audit.
- Flash loan and oracle-related exploit context: Chainlink Education Hub — What Is a Blockchain Oracle? — cited to support the explanation of oracle dependence and manipulation risk in DeFi systems.
- Static analysis and audit tooling: Slither — cited as a leading static analysis tool used in professional smart contract reviews.
- Fuzzing-based smart contract testing: Echidna — cited to support the explanation of fuzz testing as part of higher-assurance audit workflows.
- Formal verification tooling: Certora Prover — cited as a reference for formal verification and mathematical rule-checking in advanced smart contract review.
- Blockchain security incident reporting: Rekt News — cited as a public reporting source for major DeFi exploits and incident context referenced in security discussions.
Smart Contract Audit · Editorial Standards
Our Editorial Standards
Tech Capital Hub applies Google’s E-E-A-T framework to every beginner-friendly crypto guide, favoring plain-English explanations, public data, and official documentation over hype or unsupported claims. This guide shows you how to read a smart contract audit without any coding knowledge — covering DeFi security risk, audit severity levels, and the credible firms worth trusting like Trail of Bits, OpenZeppelin, and Spearbit. It leans on trusted references where they support specific points, including block explorers like Etherscan for verifying deployed code and commit hashes, plus the 2026 OWASP Smart Contract Top 10 for current vulnerability categories. Where audit outcomes are uncertain, we say so plainly rather than overstate safety.
View how our editorial standards apply to this article
Written for Total Newcomers, Step by Step
This guide meets beginners exactly where they are. It starts with the honest reality that most people freeze when they open an audit PDF full of code — then walks through what to actually look for instead. You don’t need to read Solidity. Everyday framing anchors every lesson, from why a fresh audit matters to how a single unresolved finding can put your money at risk, so the ideas stick and you feel capable from the first check.
Audit Reports Explained Without the Jargon
Coverage breaks down the concepts that matter most, in plain language. It clarifies how a smart contract audit works, what access control, reentrancy, and oracle manipulation really mean, and how severity levels — Critical, High, Medium, Low — signal real danger. Every term is defined before it’s used, and the five simple questions worth asking are spelled out clearly so you know exactly what a strong report should show.
Official Docs and Named Sources Where They Fit
Specific claims are anchored to trusted references. Audit practices draw on named firms like Trail of Bits, OpenZeppelin, and Spearbit, vulnerability categories follow the 2026 OWASP Smart Contract Top 10, and code verification steps point to Etherscan for checking deployed contracts and matching the audited commit hash. We avoid promotional content and unverified numbers, favoring primary documentation and recognized security standards for every point.
Honest About What an Audit Can’t Promise
We state the hard truths plainly: an audit reduces risk, but it never removes it. Audited protocols have still lost enormous sums, so a badge on a homepage means little on its own. What matters is who audited it, when, what they found, and whether every issue was fixed. Because code and threat patterns change fast, this guide is reviewed and updated over time. Nothing here is financial or investment advice. Corrections or source challenges can be sent to editorial@techcapitalhub.com.
Blockchain · About the Author
Marcus Delray
Fintech Analyst · Founder of Tech Capital Hub
Marcus Delray is a fintech analyst and the founder of Tech Capital Hub. In this guide, he explains how to read a smart contract audit in plain English, what red flags matter most before investing in a DeFi protocol, and how non-developers can verify whether an audit is recent, credible, and actually relevant to the code running on-chain.
View full author bio, credentials, and links
Marcus Delray has spent over a decade researching financial technology. He built Tech Capital Hub to make complex topics useful for everyday readers, investors, founders, and operators who need practical explanations instead of jargon. His coverage focuses on blockchain, DeFi, fintech infrastructure, AI in finance, and business tools, with an emphasis on clarity, usefulness, and risk awareness.
For this guide, Marcus focuses on one of the most misunderstood parts of DeFi due diligence: the smart contract audit. Rather than assuming readers can interpret raw Solidity code, he breaks down what an audit is supposed to do, how to read the executive summary and severity breakdown, why the “Action Taken” column matters, how to verify deployed contract code on public explorers, and why an audit badge alone should never be mistaken for proof of safety. He also explains common vulnerability categories like access control failures, business logic flaws, oracle manipulation, flash loan exploits, and reentrancy in plain language. All articles are educational information, not financial, legal, or investment advice.
- Explains smart contract audit concepts in plain language for non-developers and retail DeFi readers
- Breaks down how to evaluate severity ratings, unresolved findings, audit recency, and review credibility
- Clarifies core DeFi security risks including access control flaws, reentrancy, oracle manipulation, and flash loan attacks
- Shows readers how to verify deployed contract code, check public audit reports, and compare commit hashes against live implementations
- Grounds coverage in public documentation, recognized security standards, and practical due diligence rather than hype
Enjoying our content?
Click below to add us as a preferred source. Google will prioritize our latest articles in your Top Stories, AI Mode, and AI Overviews.
Preferred Source on Google